By Eric Andrew Kristof, RN, CAHIMS | Healthcare IT Professional | HIMSS Arkansas Chapter Member
About This Series: The HIMSS Word of the Day is a running blog series drawing from the HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025) — the authoritative reference for healthcare IT professionals and the primary study resource for CAHIMS and CPHIMS certification. Each post paraphrases the term in plain language, grounds it in real-world healthcare IT context, and adds a bedside nursing perspective you won’t find in a textbook.
📖 The Term: Software as a Service (SaaS)
Source: HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025)
🔍 Plain-Language Definition
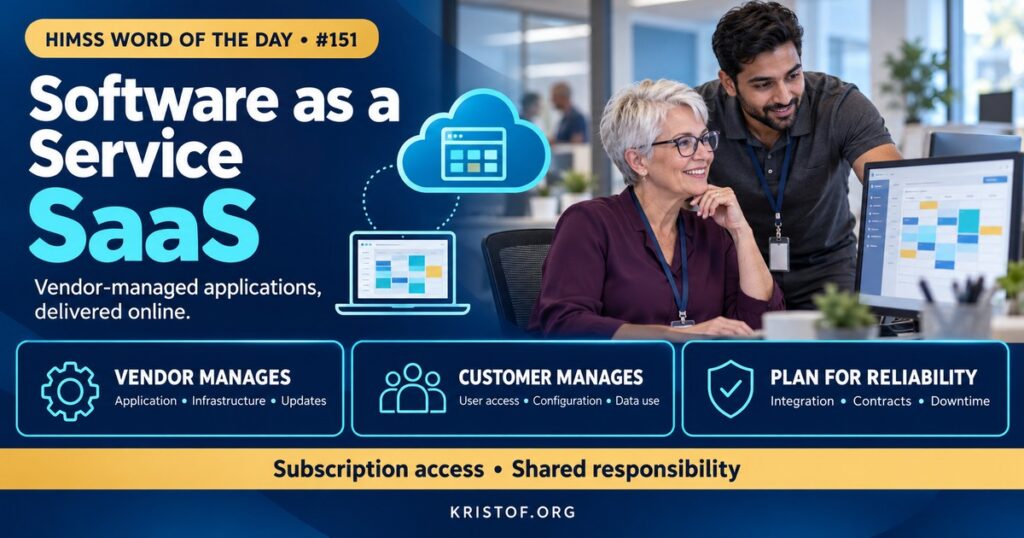
Software as a service (SaaS) is a model in which a vendor hosts and manages an application and delivers it to customers over the internet, usually through a web browser or lightweight client, typically on a subscription basis.
The HIMSS Dictionary describes SaaS as software that one or more providers deliver and manage remotely, and notes that it is also called on-demand software.
| Cloud Service Model | What the Customer Gets | What the Customer Manages | Healthcare Example |
|---|---|---|---|
| IaaS (Infrastructure as a Service) | Virtual servers, storage, networks | Operating systems, applications, data | Hosting a data warehouse on cloud servers |
| PaaS (Platform as a Service) | A platform for building and running applications | Applications and data | Developing a custom app on a cloud platform |
| SaaS (Software as a Service) | A complete application managed by the vendor | Users, configuration, data use | A cloud-based scheduling or patient engagement tool |
| On-Premises | Software installed in the organization’s own data center | Everything | A locally hosted legacy system |
⚠️ Exam Alert: In SaaS, the vendor manages the application and infrastructure; the customer still manages user access, configuration, and appropriate data use. NIST’s cloud definition identifies SaaS, PaaS, and IaaS as service models. A SaaS vendor handling PHI is generally a business associate and needs a BAA.
🌐 Why It Matters: Real-World Healthcare IT Context
SaaS has become a common way to deliver health IT. Many organizations use SaaS for human resources, scheduling, patient engagement, telehealth, analytics, revenue cycle tools, and collaboration, and many EHR vendors offer hosted or cloud-based options. Small practices often rely almost entirely on SaaS because they lack data centers and IT staff.
The benefits are practical. SaaS reduces the need for local servers and infrastructure staff, lets organizations start quickly, spreads costs into predictable subscriptions, and provides regular updates without large upgrade projects. Vendors can apply security patches across all customers at once.
NIST’s definition of cloud computing, SP 800-145, describes SaaS as the capability to use a provider’s applications running on cloud infrastructure, where the customer does not manage the underlying infrastructure, apart from limited application configuration settings.
Security follows a shared responsibility model. The vendor secures the infrastructure and application, while the customer remains responsible for who has access, how accounts are protected, how the application is configured, and what data is entered or exported. Many cloud data exposures stem from misconfigured settings or compromised user accounts rather than failures of the vendor’s infrastructure.
HIPAA applies. HHS guidance on cloud computing explains that a cloud service provider that creates, receives, maintains, or transmits ePHI on behalf of a covered entity is a business associate, even if it cannot view encrypted data. Organizations must sign business associate agreements, assess vendor risks, and include SaaS applications in their security risk analysis.
Vendor and concentration risk deserve attention. When many organizations depend on the same vendor, an outage or cyberattack can affect healthcare broadly. The 2024 cyberattack on Change Healthcare, a major claims processing and clearinghouse company, disrupted payments and pharmacy transactions across the country and highlighted how dependent healthcare has become on third-party services.
Contracts matter. Service level agreements define uptime, support response, and remedies. Contracts should also address data ownership, data return or export when the relationship ends, breach notification, audit rights, and where data is stored.
Integration remains the customer’s job. SaaS applications must exchange data with the EHR, identity systems, and other tools, usually through APIs or interfaces. Organizations that adopt many disconnected SaaS products can end up with fragmented data, duplicate logins, and information that never reaches the clinical record. An enterprise architecture review before purchase helps ensure each new tool fits into the broader system.
Total cost of ownership changes rather than disappears. Subscription fees replace capital purchases, but integration, configuration, training, and identity management still require internal effort, and subscription costs can rise over time.
Common SaaS risks in healthcare:
- Misconfigured access and sharing settings
- Weak authentication on cloud accounts
- Vendor outages affecting clinical or business operations
- Unclear data ownership and exit terms
- Shadow IT, where departments adopt SaaS without review
- Limited visibility into vendor security practices
Practices for safe SaaS adoption:
- Security and privacy review before purchase
- Business associate agreements and strong contract terms
- Single sign-on and multifactor authentication
- Inclusion of SaaS tools in risk analysis and inventories
- Downtime plans for critical SaaS applications
- Ongoing vendor monitoring and access reviews
🏥 The Nurse’s Perspective: Clinical, Bedside, & Workflow
Nurses use SaaS tools daily, often without knowing where the software runs.
At the Bedside
Cloud-based applications may support staffing and scheduling, patient education, telehealth, secure messaging, and reference resources. When these tools are unavailable, nurses need to know the downtime alternatives, just as they do for the EHR.
Approved tools matter. Using personal or free online services to store patient lists, photos, or notes creates risk because those services are not covered by business associate agreements or organizational controls.
In Clinical Workflow
Single sign-on and multifactor authentication protect SaaS accounts. Nurses should treat cloud application logins with the same care as EHR credentials, never sharing them and reporting unexpected login prompts.
Departments sometimes discover helpful SaaS products and want to adopt them quickly. Routing these requests through IT and privacy review ensures that patient data stays protected and that the tool can integrate with existing systems.
Because SaaS vendors update software frequently, screens and features may change with little notice. Release notes, brief tip sheets, and super user communication help nurses adapt without disrupting care.
Patient-facing SaaS tools, such as appointment reminders and digital check-in, also affect nursing work. When those tools fail or send incorrect information, nurses often hear about it first from patients, so reporting problems quickly helps teams correct them.
In EHR Implementation (Go-Live Perspective)
Many Epic implementations today are hosted by the vendor or a partner rather than in a local data center. Go-Live planning includes connectivity, performance testing, and downtime procedures that account for the hosted environment.
At-the-elbow support analysts often help nurses with access to connected cloud applications, such as staffing or education tools, linked through single sign-on. Quickly resolving access problems prevents workarounds and keeps workflows intact.
🎓 CAHIMS / CPHIMS & HIMSS Perspective
CAHIMS Exam Domain Mapping
SaaS appears in infrastructure, security, and vendor management questions:
| CAHIMS Domain | How SaaS Appears |
|---|---|
| Healthcare & Technology Environments | Cloud service models; vendor market; HIPAA guidance on cloud computing |
| Clinical Informatics | Cloud-based clinical tools, downtime plans, user experience with updates |
| Healthcare Information & Systems Management | Shared responsibility, integration, identity management, data export |
| Management & Leadership | Contracts, SLAs, total cost of ownership, vendor risk management |
Key Terms to Know Alongside SaaS
- Cloud Computing — on-demand access to shared computing resources over a network
- IaaS and PaaS — cloud models providing infrastructure or development platforms
- Shared Responsibility Model — the division of security duties between vendor and customer
- Service Level Agreement (SLA) — contractual commitments for availability and support
- Business Associate Agreement (BAA) — the HIPAA contract required for vendors handling PHI
- Shadow IT — technology adopted without IT or security approval
HIMSS Organizational Position
HIMSS addresses cloud adoption and third-party risk through its cybersecurity education, research, and Healthcare Cybersecurity Community, encouraging strong vendor management and shared responsibility. Members can find related education and research through the HIMSS Resource Center.
🔗 Explore Further: External References
- NIST — SP 800-145, The NIST Definition of Cloud Computing https://csrc.nist.gov/pubs/sp/800/145/final
- HHS — Guidance on HIPAA and Cloud Computing https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html
- HHS — Business Associates https://www.hhs.gov/hipaa/for-professionals/privacy/guidance/business-associates/index.html
- FedRAMP https://www.fedramp.gov/
- HHS — Change Healthcare Cybersecurity Incident Frequently Asked Questions https://www.hhs.gov/hipaa/for-professionals/special-topics/change-healthcare-cybersecurity-incident-frequently-asked-questions/index.html
- HIMSS — Healthcare Cybersecurity Community https://www.himss.org/networking/communities/healthcare-cybersecurity/
Term source: HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025). All definitions in this series are paraphrased for editorial purposes. Readers are encouraged to consult the primary source for exact language.
Eric Andrew Kristof, RN, CAHIMS is a Healthcare IT professional and HIMSS Arkansas Chapter member based in Hot Springs Village, AR, with hands-on Epic Go-Live experience and a diverse healthcare and IT background. He writes at kristof.org at the intersection of clinical care and healthcare technology.
Leave a Reply