By Eric Andrew Kristof, RN, CAHIMS | Healthcare IT Professional | HIMSS Arkansas Chapter Member
About This Series: The HIMSS Word of the Day is a running blog series drawing from the HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025) — the authoritative reference for healthcare IT professionals and the primary study resource for CAHIMS and CPHIMS certification. Each post paraphrases the term in plain language, grounds it in real-world healthcare IT context, and adds a bedside nursing perspective you won’t find in a textbook.
📖 The Term: Accounting of Disclosures
Source: HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025)
🔍 Plain-Language Definition
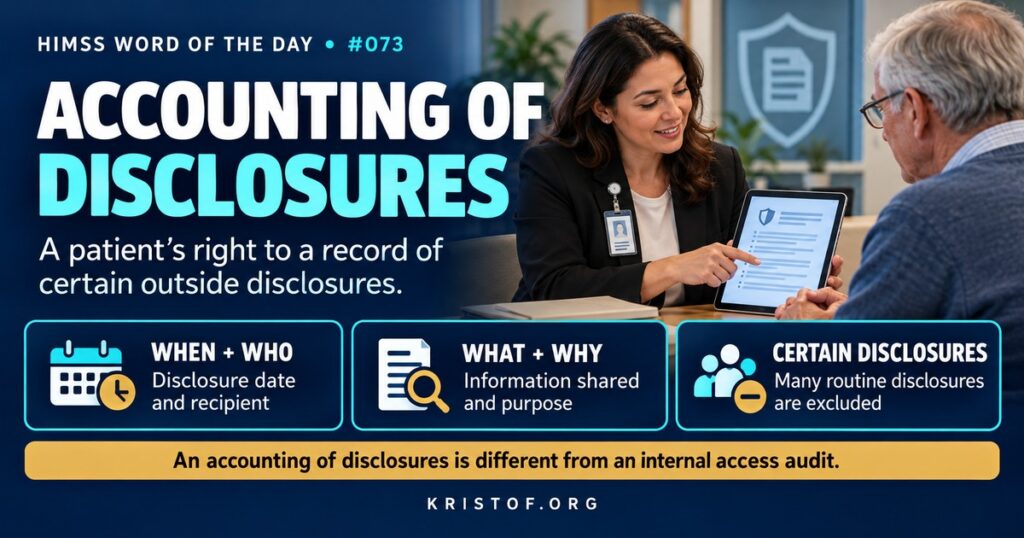
The accounting of disclosures is a right under the HIPAA Privacy Rule that allows a person to ask a covered entity for a list of certain disclosures of their protected health information, meaning instances when information was shared outside the organization, and to whom, when, and why.
The HIMSS Dictionary explains that individuals may receive an accounting of disclosures of their protected health information that a covered entity made during the six years before the request, subject to exceptions found in the HIPAA regulations at 45 CFR 164.528.
The exceptions are where most of the nuance lies. The accounting does not include many routine disclosures, so it is far from a complete record of everyone who saw a patient’s information.
| Generally Included in an Accounting | Generally Excluded From an Accounting |
|---|---|
| Disclosures for certain public health activities | Disclosures for treatment, payment, and health care operations |
| Disclosures required by law, such as certain reports | Disclosures to the individual about themselves |
| Disclosures for judicial or administrative proceedings | Disclosures made under the individual’s authorization |
| Certain disclosures to law enforcement | Facility directory and disclosures to people involved in care |
| Disclosures for research without authorization, with special rules | Disclosures for national security or to correctional institutions in specified situations |
| Impermissible disclosures, such as a misdirected record | Disclosures that are part of a limited data set |
For each included disclosure, the accounting generally lists the date, the recipient, a brief description of the information, and the purpose.
⚠️ Exam Alert: An accounting of disclosures lists certain disclosures outside the organization and is a patient right. An audit trail records every access and action inside the system and is an internal security tool. An authorization is the patient’s permission for a disclosure; disclosures made under an authorization are generally excluded from the accounting. Expect a question that tests what the accounting does and does not contain.
🌐 Why It Matters: Real-World Healthcare IT Context
The accounting of disclosures supports transparency. Patients can learn when their information was sent to a public health agency, provided in response to a subpoena, reported to law enforcement, or disclosed by mistake. That knowledge can help them understand how their information moves and identify disclosures they did not expect.
Tracking disclosures is mostly the work of health information management (HIM) and release-of-information teams. Many included disclosures, such as responses to subpoenas or requests from attorneys, flow through those teams and can be logged as they occur. Others, such as mandatory public health reports sent automatically from the EHR, require organizations to know which reports are sent, for which patients, and when, so they can be included if a patient asks.
The HITECH Act directed HHS to expand the accounting to include treatment, payment, and health care operations disclosures made through an electronic health record. The current regulation at 45 CFR 164.528, however, still contains the long-standing exception for treatment, payment, and operations, so organizations should follow the regulation as written and watch for any future rulemaking.
Requests are relatively uncommon, but organizations must be able to respond within the timeframes the rule sets, generally within 60 days with one possible extension, and must provide the first accounting in any 12-month period without charge.
The difference between disclosures and access matters for patients’ expectations. A patient worried that a coworker or relative looked at their chart is usually asking about internal access, which the accounting does not address. In that situation, organizations typically handle the concern through the privacy office, which can review audit logs and investigate whether access was appropriate.
Common accounting challenges:
- Disclosures made outside HIM, such as reports sent directly by departments, that are never logged
- Automated public health reporting that is not tracked by patient
- Confusion between the accounting and an internal access report
- Misdirected faxes or emails that are not recorded as impermissible disclosures
- Records spread across multiple systems with no central disclosure log
- Staff unaware that certain disclosures must be tracked
Characteristics of strong disclosure tracking:
- A central disclosure log integrated with release-of-information workflows
- Automated capture of mandated reports where possible
- Clear policies on which disclosures must be logged
- Procedures for logging impermissible disclosures during breach investigations
- Templates and timelines for responding to patient requests
- Staff training that explains the difference between access monitoring and disclosure accounting
🏥 The Nurse’s Perspective: Clinical, Bedside, & Workflow
Nurses rarely prepare an accounting, but they make or initiate many disclosures that may need to be tracked.
At the Bedside
Patients sometimes ask nurses who can see their records or who has received their information. Nurses can explain that care teams within the organization use information to treat them, and that patients can request formal information about certain outside disclosures from the health information management or privacy office.
Some disclosures begin at the bedside. Reports of suspected abuse, certain communicable disease reports, or information provided to law enforcement under specific circumstances may be initiated by clinicians. Following the organization’s procedures for these situations ensures that disclosures are lawful and properly recorded.
In Clinical Workflow
Misdirected information is a disclosure risk in everyday work. A fax sent to the wrong number, an after-visit summary handed to the wrong patient, or an email with the wrong attachment may be an impermissible disclosure. Reporting these events promptly allows the privacy office to investigate, mitigate harm, decide whether breach notification is required, and record the disclosure.
Requests from outside parties, such as an attorney or an insurer asking for records, should be routed to the release-of-information process rather than handled informally on the unit.
In EHR Implementation (Go-Live Perspective)
During an Epic Go-Live, release-of-information workflows and disclosure tracking tools are configured in the new system, and automated interfaces to public health and registries are rebuilt. Teams should confirm that disclosures made through those interfaces can still be identified if a patient requests an accounting.
At-the-elbow support analysts can help clinical staff find the correct process for routing outside requests and printing records, and remind them that printing or sending information outside the organization follows defined procedures.
🎓 CAHIMS / CPHIMS & HIMSS Perspective
CAHIMS Exam Domain Mapping
The accounting of disclosures is a frequently tested HIPAA patient right:
| CAHIMS Domain | How the Accounting Appears |
|---|---|
| Healthcare & Technology Environments | HIPAA Privacy Rule patient rights; HITECH changes; enforcement |
| Clinical Informatics | Clinician-initiated disclosures; misdirected information; patient questions |
| Healthcare Information & Systems Management | Disclosure logging, release-of-information systems, interface tracking |
| Management & Leadership | Privacy policies, HIM operations, response timelines, staff training |
Key Terms to Know Alongside Accounting of Disclosures
- Disclosure — the release or sharing of information outside the entity holding it
- Use — the sharing, application, or examination of information within the entity
- Audit Trail — a record of system activity used to monitor access and changes
- Authorization — written permission for uses and disclosures not otherwise permitted
- Release of Information (ROI) — the process of responding to requests for copies of health records
- Impermissible Disclosure — a disclosure not permitted by the Privacy Rule, which may trigger breach analysis
HIMSS Organizational Position
HIMSS engages on HIPAA privacy policy, including patient rights and transparency about how health information is shared, through its public policy work. Members can find related education and research through the HIMSS Resource Center.
🔗 Explore Further: External References
- eCFR — 45 CFR 164.528, Accounting of Disclosures of Protected Health Information https://www.ecfr.gov/current/title-45/subtitle-A/subchapter-C/part-164/subpart-E/section-164.528
- HHS — Summary of the HIPAA Privacy Rule https://www.hhs.gov/hipaa/for-professionals/privacy/laws-regulations/index.html
- HHS — Breach Notification Rule https://www.hhs.gov/hipaa/for-professionals/breach-notification/index.html
- HHS — Uses and Disclosures for Treatment, Payment, and Health Care Operations https://www.hhs.gov/hipaa/for-professionals/privacy/guidance/disclosures-treatment-payment-health-care-operations/index.html
- AHIMA — American Health Information Management Association https://www.ahima.org/
- ONC — Health IT Legislation https://healthit.gov/legislation/
Term source: HIMSS Dictionary of Health Information and Technology Terms, Acronyms, and Organizations, 6th Edition (2025). All definitions in this series are paraphrased for editorial purposes. Readers are encouraged to consult the primary source for exact language.
Eric Andrew Kristof, RN, CAHIMS is a Healthcare IT professional and HIMSS Arkansas Chapter member based in Hot Springs Village, AR, with hands-on Epic Go-Live experience and a diverse healthcare and IT background. He writes at kristof.org at the intersection of clinical care and healthcare technology.
Leave a Reply